

Southern Telematics Company Fends Off Powerful DDoS Attack With Linx Cloud
The coordinated response by the company’s team and the provider’s cybersecurity professionals helped restore operations quickly.
Modern DDoS attacks against enterprise infrastructure are highly intensive and rely on multiple techniques used by attackers. Defending against them requires a comprehensive security strategy as well as close coordination among information security teams.
More Than 273,000 Bots Joined the Attack
In September, the infrastructure of Yuzhnaya Telematicheskaya Kompaniya (Southern Telematics Company) came under a targeted attack. The Linx team helped identify the incident. Its employees detected a sharp increase in traffic on one of the company’s channels. Diagnostics confirmed that the surge was caused by a DDoS attack. The attackers made several attempts to bypass the filters, changing their attack vector each time. According to cybersecurity professionals, this indicates that the hackers were deliberately targeting the company. Peak attack traffic reached 378 Gbps, while the number of bots used in the attack exceeded 273,000.
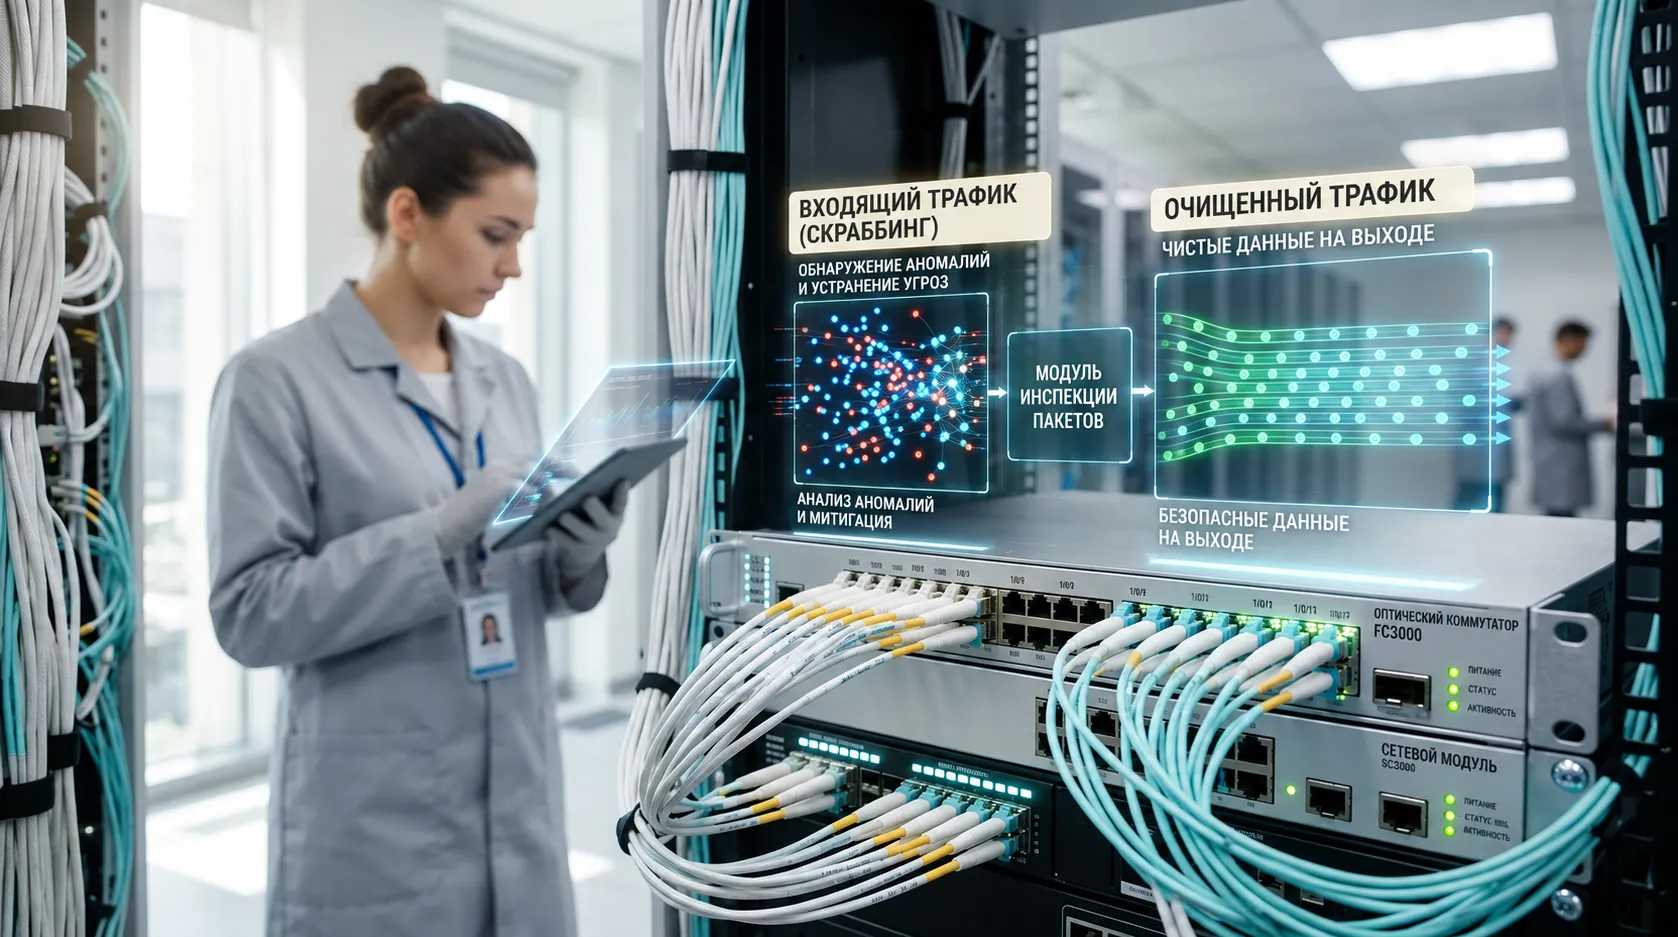
To restore the client’s operations, the Linx team decided to isolate the traffic under attack and redirect it to the filtering infrastructure of StormWall, Linx Cloud’s information security partner. From detecting the anomaly to launching the Anti-DDoS cloud service and beginning traffic scrubbing, the Linx Cloud team took about three hours.
The Impact Was Minimized
Employees of Yuzhnaya Telematicheskaya Kompaniya also played an active role in mitigating the attack. The company deployed network engineers and server administrators. Rapidly activating DDoS protection and configuring customized security policies allowed the company to restore its services as quickly as possible.
“Thanks to the coordinated efforts of Linx Cloud and our cybersecurity professionals, we were able to minimize the impact of the DDoS attack and quickly restore our systems. We view this incident as confirmation of the reliability of the provider we selected,” said Pavel Komarov, IT Director of Yuzhnaya Telematicheskaya Kompaniya.
This case is instructive: cloud providers and specialized Anti-DDoS operators can bring additional capacity online while an incident is already underway. This approach can limit the damage caused by attackers and help organizations restore critical services faster.
Breach Attempts Are Becoming More Sophisticated
Comprehensive DDoS protection is becoming increasingly important as the number of attempts to breach corporate infrastructure continues to rise. According to Kaspersky DDoS Protection, the number of DDoS attacks in Russia and the CIS increased by 27% from January through May 2026 compared with the same period in 2025.
Experts also point to a shift in the nature of these attacks: they are becoming more sophisticated and lasting longer. Attackers imitate legitimate user sessions, including logins, searches and order placement, making them significantly harder to detect with traditional IP-based filtering and connection-rate limits. Telecommunications companies, financial institutions and government organizations are the most frequent targets.
The intensity of breach attempts has been rising for several years. In 2022, for example, CloudMTS mitigated a multiday DDoS attack against the infrastructure of a client at a Moscow data center. Peak traffic reached 30 million flows per second. To handle the incident, the provider brought in a specialized Anti-DDoS partner.
The Future of Anti-DDoS as a Service
In 2025, a DDoS attack targeting media outlets in Russia’s Kursk region lasted more than 49 hours. Some websites became inaccessible or experienced delays. Access to the affected resources was restored only after additional capabilities of the Center for Monitoring and Management of the Public Communications Network were activated.
The Yuzhnaya Telematicheskaya Kompaniya case once again demonstrated the need for a comprehensive approach to protecting against modern DDoS attacks. In the coming years, the Anti-DDoS as a Service model is likely to continue expanding, with security delivered through the cloud and large distributed traffic-scrubbing centers. This model makes economic and technological sense for organizations that would struggle to maintain their own network capacity and hardware capable of absorbing hundreds of gigabits of malicious traffic.